
GravityRAT Mobile Cyber-Campaign Targets Defense Personnel

An Active Campaign Targeting Defense Personnel
Lookout has uncovered an active cyber-surveillance campaign deploying GravityRAT malware to target defense industry and military personnel. Based on Lookout telemetry, primary targets are individuals from India who are seeking lucrative positions at foreign defense contractors. Given the nature of the lure infrastructure, defense personnel in other nations may also be targeted.
Over the past 12 months, Lookout detected GravityRAT across 14 devices from India.
GravityRAT is a long-running, multi-platform surveillance framework active since at least 2015. It is attributed to Pakistan-aligned threat actors tracked under names such as SpaceCobra, and Cosmic Leopard. While initially it was a Windows-based tool, GravityRAT has expanded into a cross-platform framework capable of targeting Android, Windows, and macOS operating systems.
New Campaign Lures
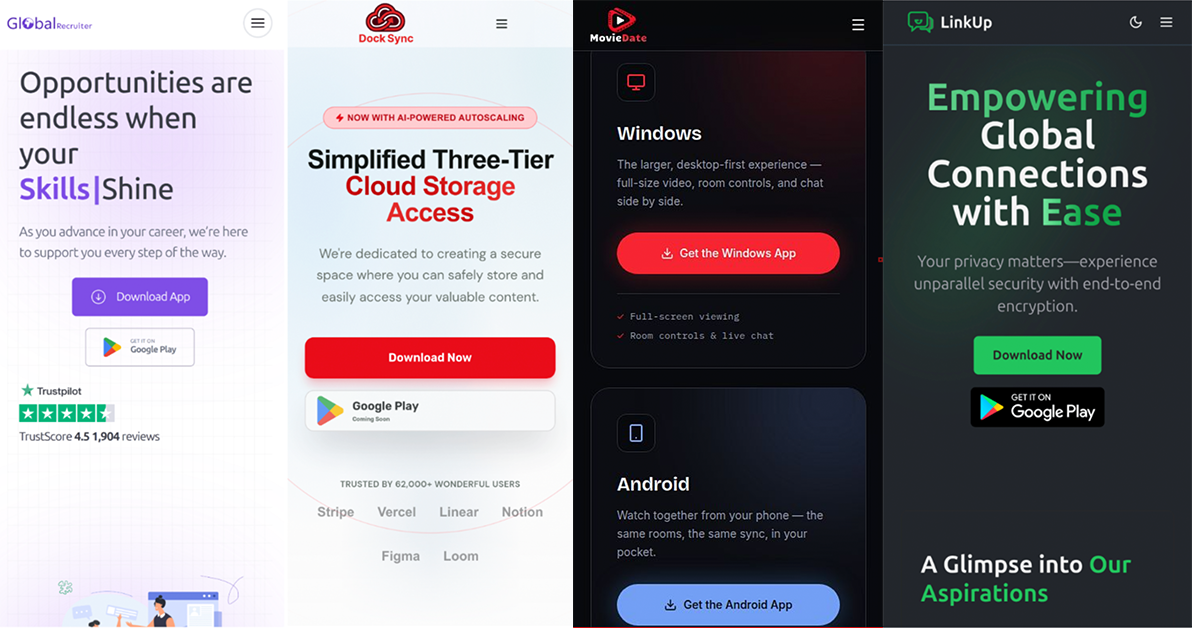
Lookout discovered several live, single-page portals, which mimic recruitment firms and commercial software utilities to distribute GravityRAT payloads. These websites feature standard web layouts, interface icons, user reviews, trust badges, and Google Play style buttons to simulate legitimate distributors.
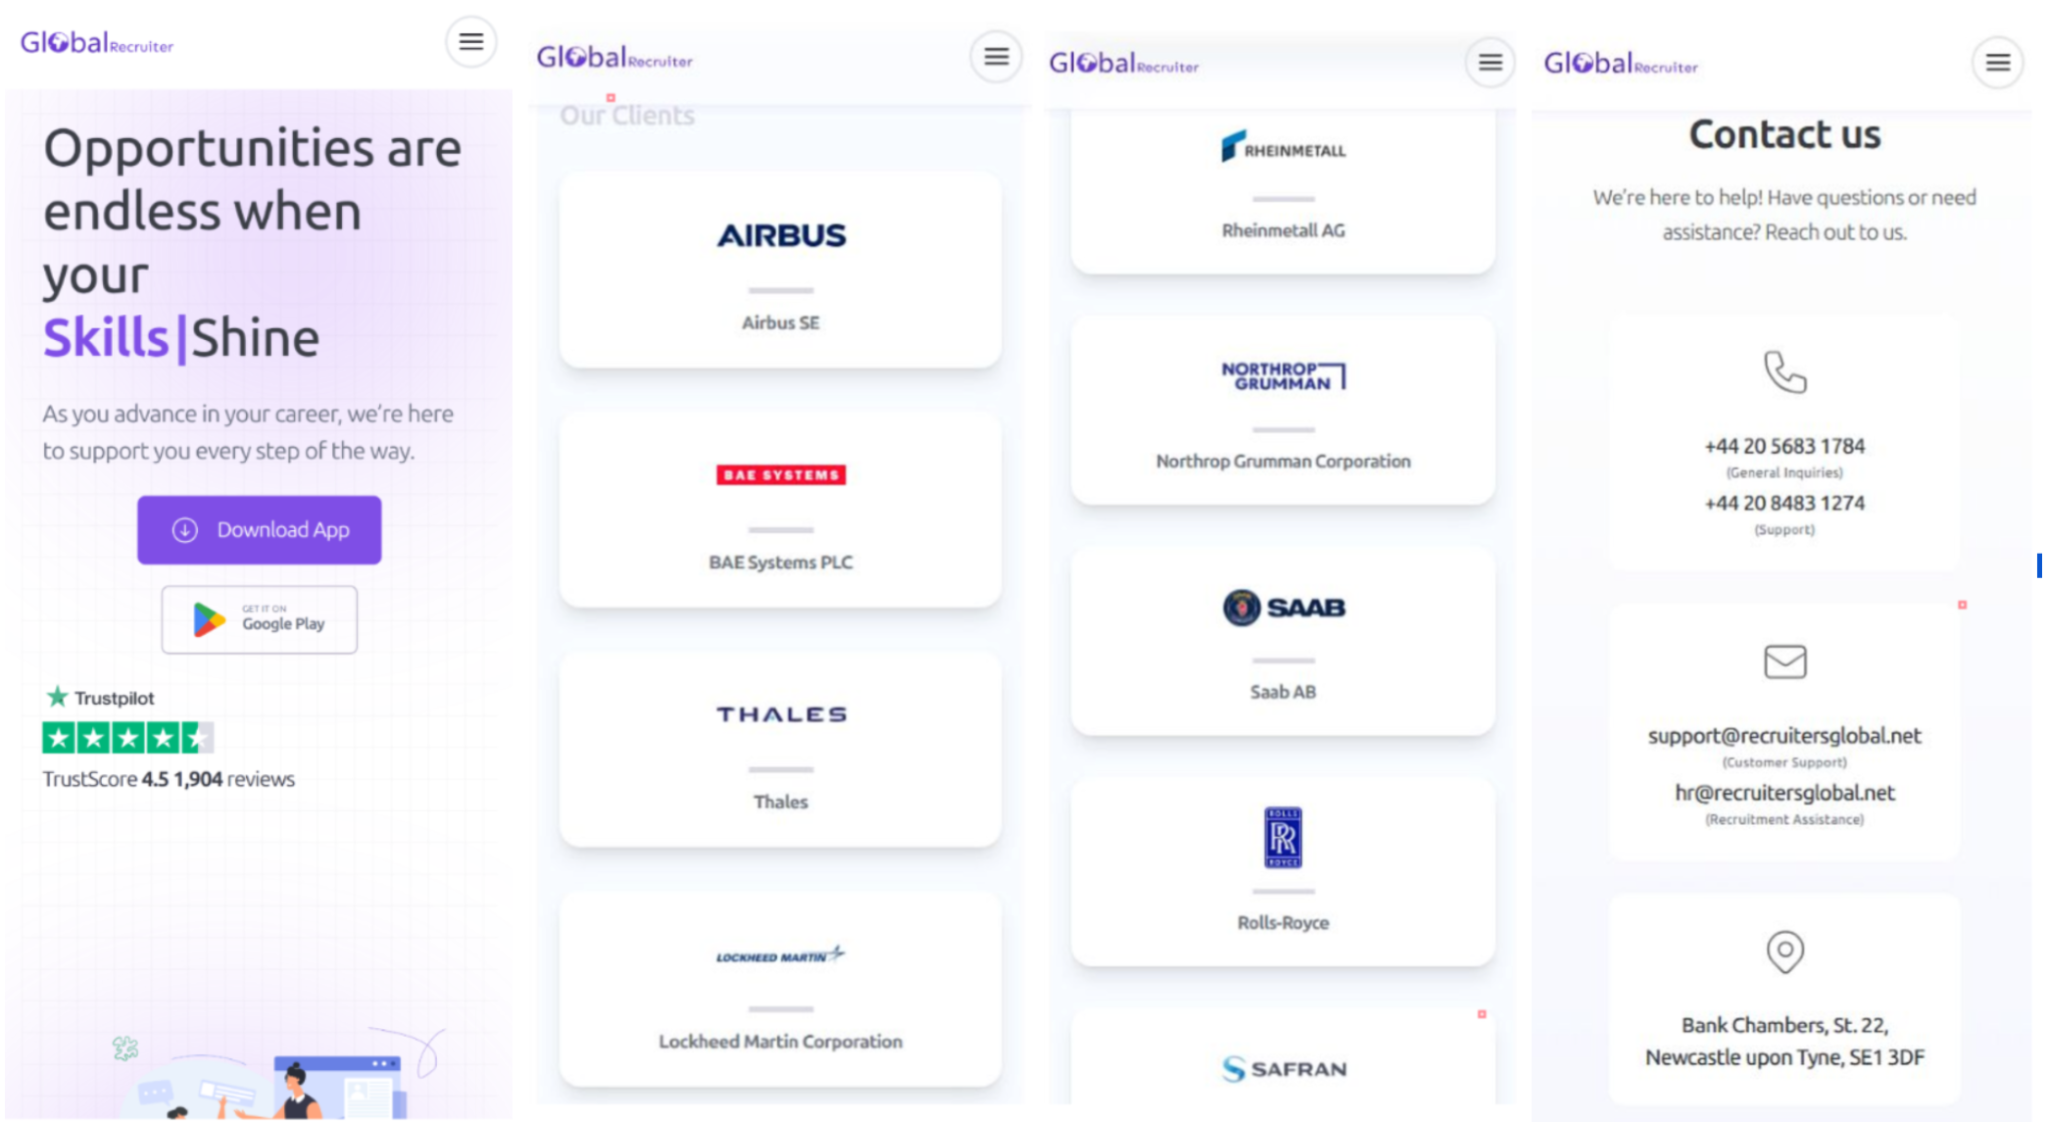
A notable example is the recruitment portal at recruitersglobal[.]net, which delivers the GravityRAT payload mobile application GlobalRecruiters.apk (com.resumee.resumebuilder). Posing as "Global Recruiter," the site offers automated resume-building tools and job connections to entice applicants.
To build credibility, the site's "Our Clients" section prominently displays logos of major international defense and aerospace leaders, including Airbus SE, BAE Systems PLC, Thales, Lockheed Martin Corporation, Rheinmetall AG, Northrop Grumman Corporation, Saab AB, Rolls-Royce, and Safran. Explicitly targeting this sector aligns directly with GravityRAT's historical focus on government and defense personnel.
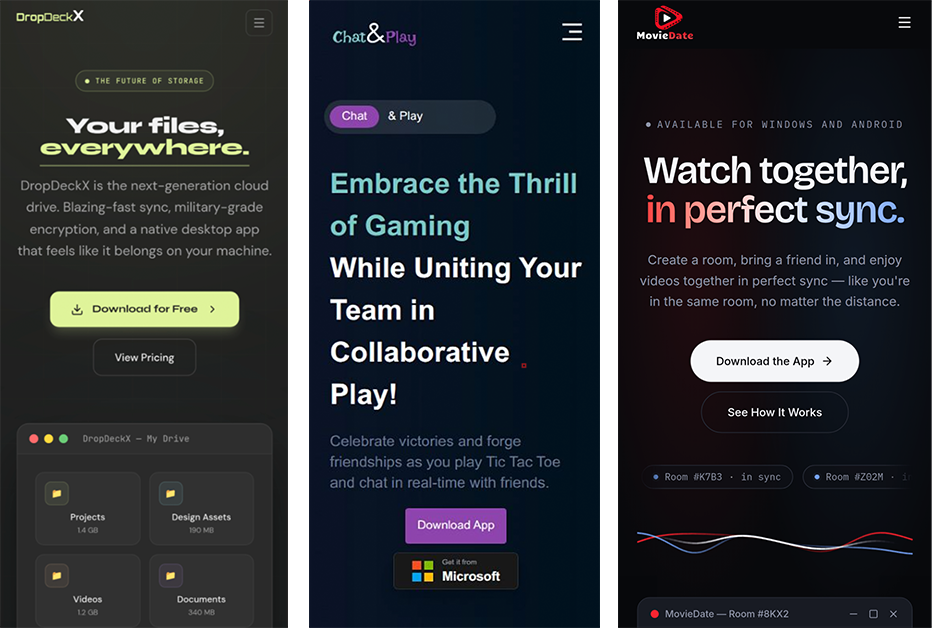
Live distribution websites identified in the most recent GravityRAT campaign.
The "App Store Coming Soon" Psychological Trick
When users click the Google Play download button on these malicious landing pages, they do not reach the official Google Play Store. Instead, a custom pop-up dialog appears with a notice stating: "The Google Play version is currently under review. Please download the APK for now."
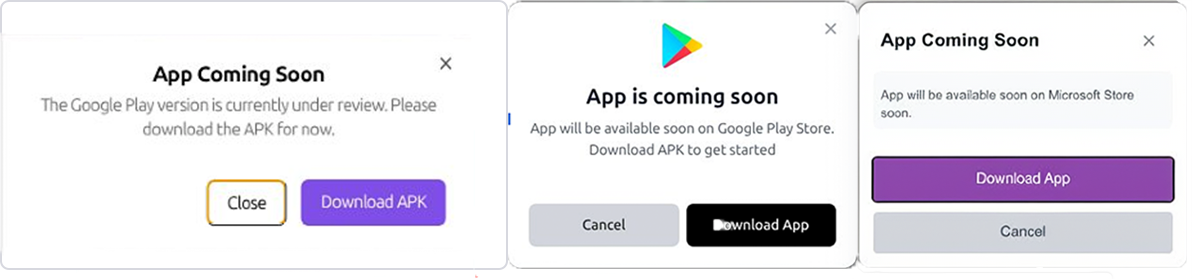
This technique provides a plausible explanation for the need to sideload this app (eschewing the safety of only installing apps from Google Play) to bypass an alleged delay. The apps that we described in this article were not found to be distributed through Google Play.
Capabilities
GravityRAT is designed for extensive and periodic data exfiltration, functioning autonomously to upload collected data to C2 servers on their PHP endpoints at intervals ranging from 1 to 30 minutes.
Collected victim data types include:
- Complete contact directory dumps
- Incoming, outgoing, and missed call logs
- Historical and real-time SMS messages
- GPS location coordinates
- External storage directory trees and files
- Document, image & audio files with extension .pdf, .doc, .docx, .xls, .xlsx, .ppt, .pptx, .txt, .jpg,.jpeg .png, .log, .txt, .xml and .opus
- Encrypted WhatsApp backup databases (specifically targeting extensions .crypt12, .crypt13, .crypt14, .crypt18, and .crypt32)
- Connected Wi-Fi network details, device accounts, and hardware IMEI identifiers
By pivoting across live infrastructure associated with mobile builds that shared identical name servers and registration dates, we uncovered other malicious domains like dropdeckx[.]com. This domain advertises a Windows executable file with a similar single page website and a cloud storage utility lure identical to those previously utilized by GravityRAT threat actors. It is an Electron-based cloud storage utility called DropDeckX that evades virtual machines, harvests system telemetry and credentials, establishes persistence via Task Scheduler, and downloads secondary payloads. The sample uses the subdomain web.dropdeckx[.]com as its C2 server. Similar variants of this malware have been tracked publicly as HeavyLift.
Command and Control
GravityRAT command infrastructure uses Cloudflare-protected domains. Implants route exfiltrated log data to PHP backend handling scripts hosted on subdomains disguised as legitimate Android frameworks. Active endpoint URLs identified include:
- an-east.androidannotations[.]com/vanilla/B67j96dg.php
- api.androidwebsys[.]com/delta/X25r87Nf.php
- meta.androidasynclib[.]com/azure/H54F257gd4.php
- static.androidufslib[.]com/hotel/H28j75Ft.php
- connectivity.androidstaticserve[.]com/blue/B67j96dg.php
- api.androiddevpool[.]com/mike/B67j96dg.php
Indicators of Compromise
SHA1
ce2ce25cbe461af221cf215b3c67bf531cf74855
1567801b0614d814ea681867891d2fb4c68a5f3b
4b1c78f35510f77d896014cabbed8bfd3c5a4fdf
c48b72f248f4ffea3e2dc960331a19556acb9256
a80af5b2f0c5ff71e4384dc273822eda28068878
10a8fcb42993fa75310a4767c03d89c5aac86e10
1aba3697a090e0be0dc8dbab4987c6bc585629ef
14a2177bf319f1d592b31153ab39526312c939ae
bbbdcb8a7f25c1b1345f54c95049eb8b1cea10ab
86683d68c942326d9f547bd6878a4da43e9eceb3
9ffe46c3a2c8b3131084e881e0cd2554e2d7f93d
Domains
recruitersglobal[.]net
movie-date[.]net
dock-sync[.]com
dropdeckx[.]com
linkuptoday[.]net
androiddevpool[.]com
androidannotations[.]com
androidwebsys[.]com
androidasynclib[.]com
androidufslib[.]com
androidstaticserve[.]com
cloudupnext[.]com
myvaultz[.]com
chatnplay[.]in
Authors
Parth Bhatt
Giampaolo Dedola


