
The Mobile Blind Spot: Securing AI Across Financial Services & Insurance
Stopping AI-Driven Social Engineering at the Mobile Edge: Unifying Human Threat Protection, App Exposure Control and AI Governance
Generative AI and voice-cloning technologies have fundamentally altered the economics of cyber offense in the financial services and insurance sectors. Rather than trying to breach hardened corporate networks, threat actors now exploit the human element on mobile channels. Armed with linkless conversational AI, synthetic voice deepfakes, and multi-channel smishing (SMS, WhatsApp, Signal), attackers target wealth managers, underwriters, and claims adjusters where enterprise scrutiny is lowest.
Agenda & Format
Opening & The Mobile Risk Shift
- The Invisible Attack Surface: Why hardened corporate firewalls mean little when modern financial advisors, underwriters, and adjusters operate primarily on unmonitored mobile devices.
- The AI Acceleration: How generative AI and voice-cloning tools have fundamentally rewritten the economics of financial fraud and mobile attacks.
Neutralizing Mobile Social Engineering
- Beyond Email Gateways: Defending against non-link, multi-channel smishing across SMS, WhatsApp, and Signal.
- Voice Deepfakes & Vishing: Detecting synthetic voice cloning and executive impersonation to prevent wire fraud and unauthorized transfers.
- Crowdsourced Defense: Equipping employees with self-service message verification to convert your workforce into an active security layer (SEP Bundle).
Bridging the Mobile AI Governance Gap
- Shadow AI on Mobile: Identifying unapproved generative AI apps used by mobile staff that expose sensitive financial PII and client data (AI V&G).
- Agentic Workflows & App Exposure: Securing the third-party mobile apps and SDKs that drive daily financial operations.
Operational Risk & Governance Alignment
- From Compliance to Operational Resilience: Moving away from passive regulatory checklists to active threat containment.
- Leveraging Financial & Insurance Frameworks: Enforcing MFA and third-party risk controls under NYDFS Part 500, curbing off-channel communication risks under SEC/FINRA recordkeeping rules, and ensuring data privacy under GLBA and DORA.
Real-World Demonstrations & Defense in Action
- Scenario 1 (SEP Demo): Intercepting an AI voice-cloning/vishing attack targeted at a financial advisor to prevent wire fraud.
- Scenario 2 (AI V&G Demo): Real-time interception blocking an insurance adjuster from pasting sensitive customer PII into an unapproved mobile GenAI tool.
- Platform Visibility: Live demonstration of Lookout’s unified console—combining Social Engineering Protection (SEP) and AI Visibility & Governance in real time.
Why Attend?
Mitigate Mobile AI Risk
Gain complete visibility into shadow generative AI apps and unapproved SDKs accessed on mobile devices that expose high-value client PII.
Neutralize Voice Deepfakes
Learn how to defend against sophisticated, linkless conversational AI and voice-cloning executive impersonation used to bypass corporate firewalls.
Combat Advanced Smishing
See how to block cross-channel phishing attacks across SMS, WhatsApp, and Signal that completely bypass email gateway filters.
Ensure Compliance Alignment
Align your security controls with major regulatory frameworks like NYDFS Part 500, GLBA, SEC/FINRA, and DORA for active resilience.
Meet the Speaker
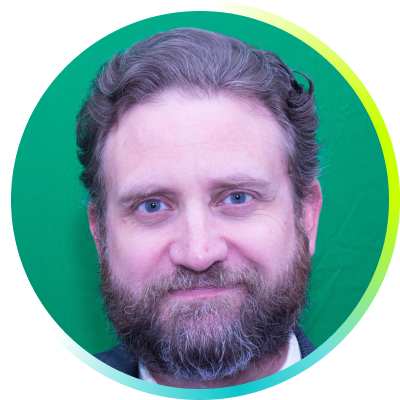
Andrew Olpin
Director of Solutions Engineering, Lookout
Andrew Olpin is an industry-recognized cybersecurity veteran specializing in mobile defense, threat intelligence, and enterprise risk management.
Secure Your Spot for the Live Webinar
Registration is free but spaces are limited. Fill out the form above to reserve your place, and prepare to transition from passive compliance to active, AI-era threat containment.
Claim Your Virtual Seat